Cyber Security M&A Audit & Review Service
Book a free no obligation informal chat
Quantifying cyber risk during mergers and acquisitions to protect deal value and accelerate integration
WHY CYBER DUE DILIGENCE MATTERS
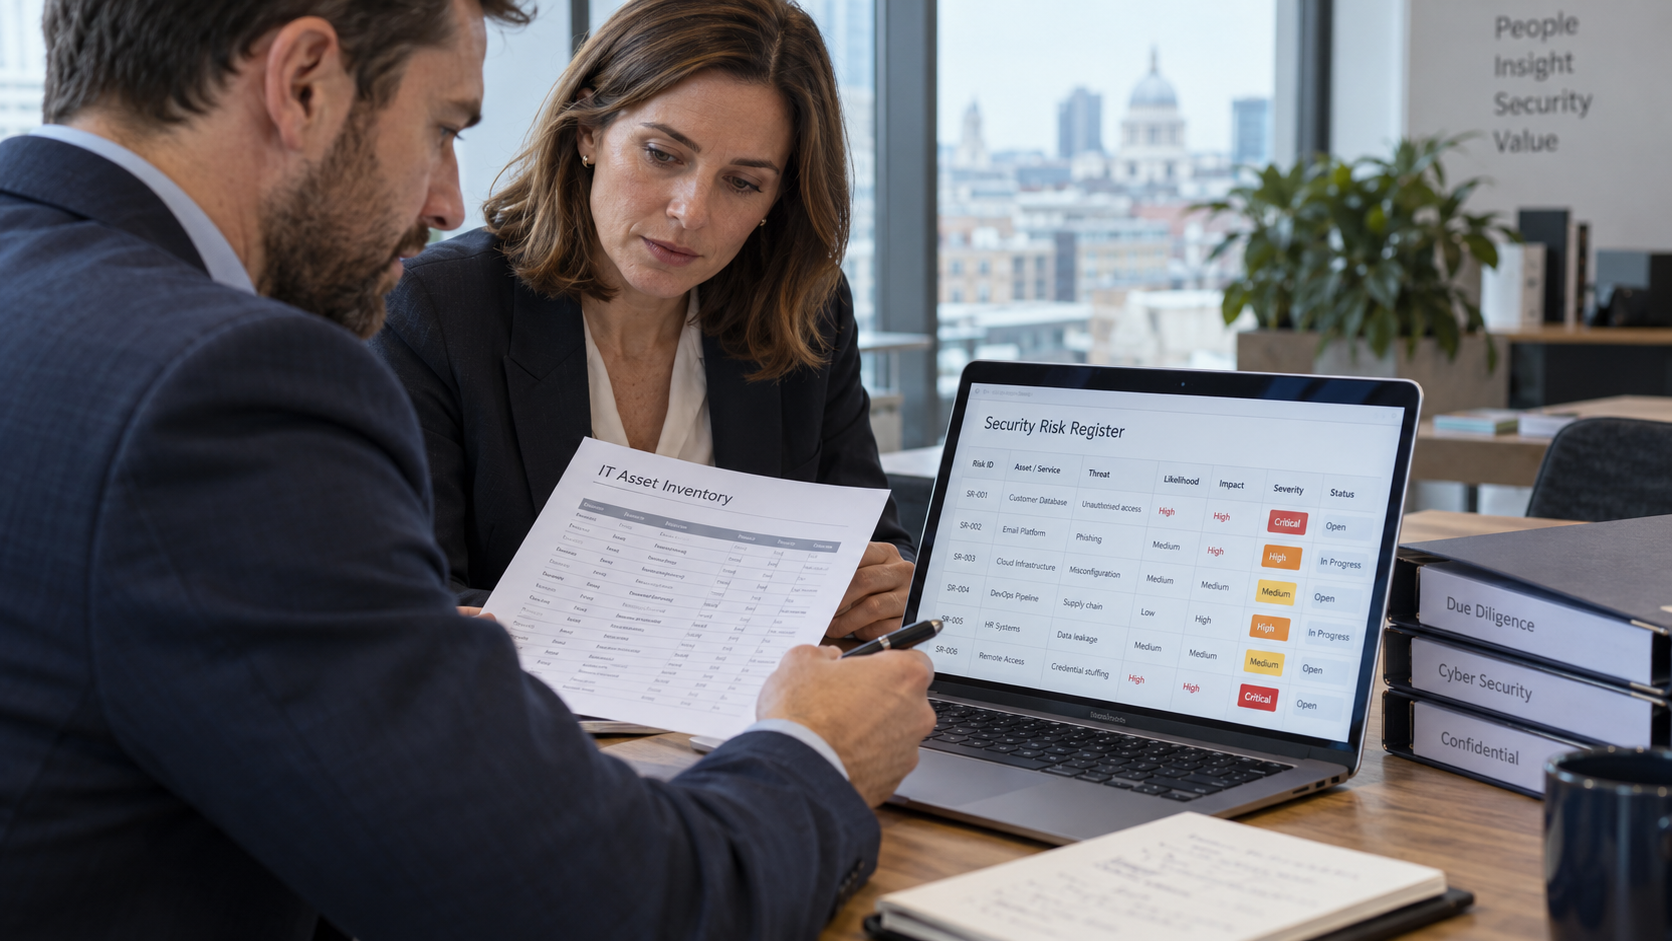
Mergers and acquisitions are no longer just financial transactions— they are also technology and data-driven events where cyber risk plays a decisive role. In today's market, failing to conduct thorough cyber due diligence can result in hidden costs, regulatory penalties, and integration challenges that directly erode deal value.
Cyber threats are now a material risk in any transaction. Hidden vulnerabilities, non-compliance issues, or weak Governance, Risk & Compliance (GRC) frameworks can:
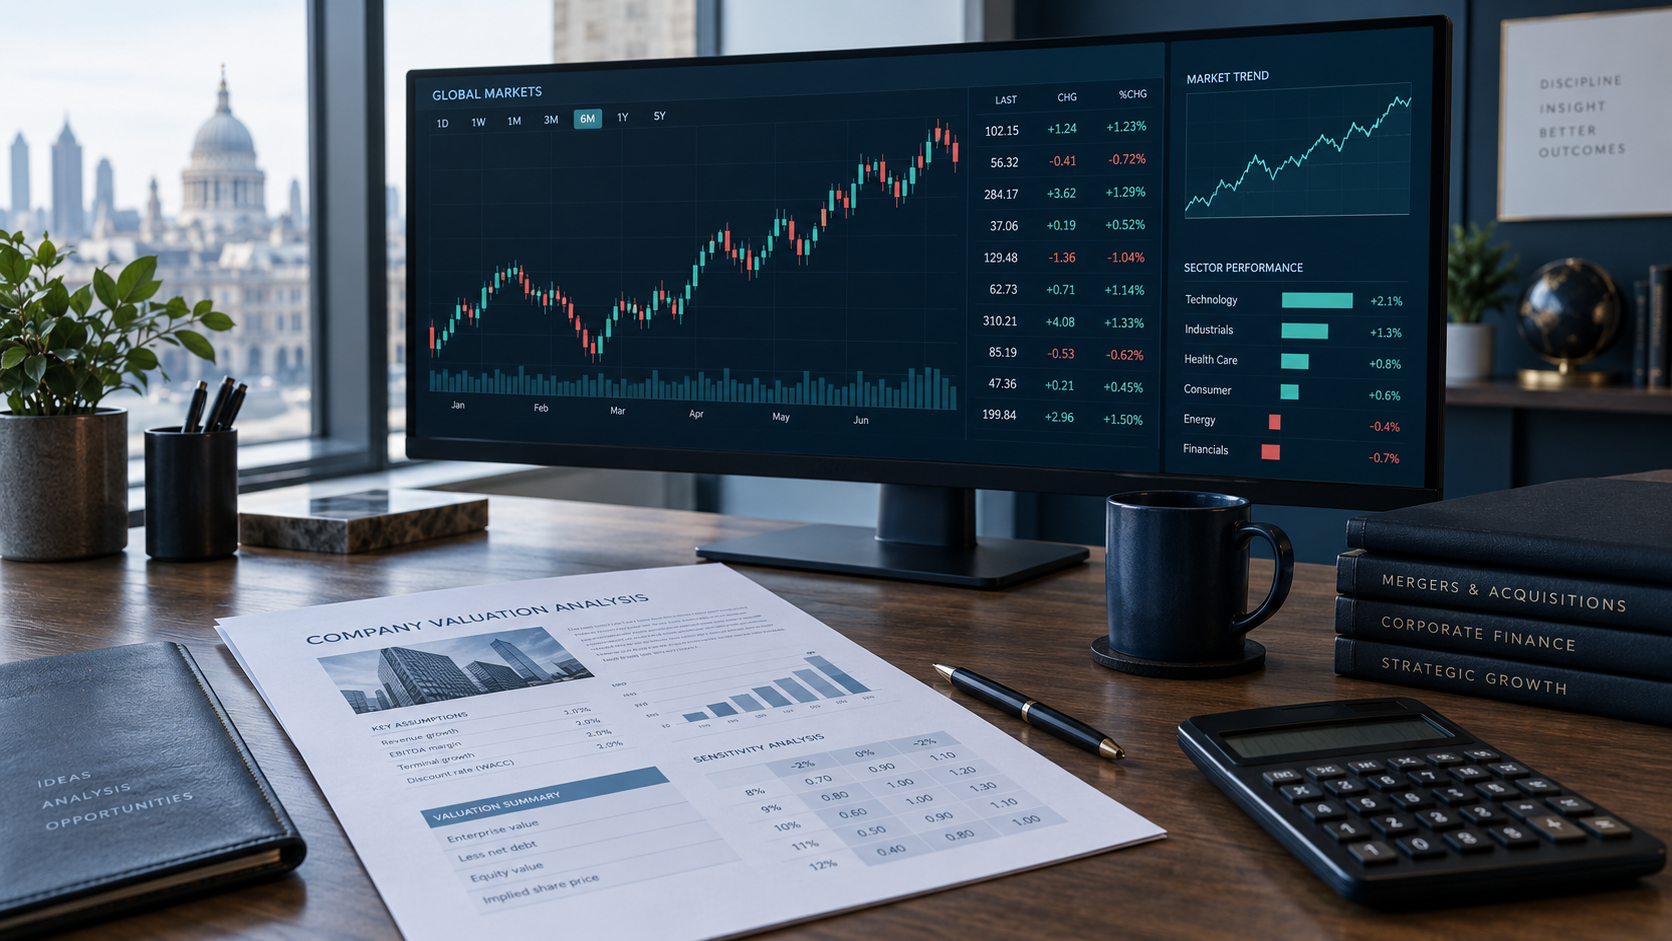
- Reduce company valuation
- Introduce hidden liabilities, such as legacy breaches, technical debt, or
contractual non-compliance - Delay or derail integration by uncovering security weaknesses late in the
process - Trigger regulatory fines and reputational damage under frameworks such as GDPR, NIS2, and DORA
OUR SERVICE OFFERING
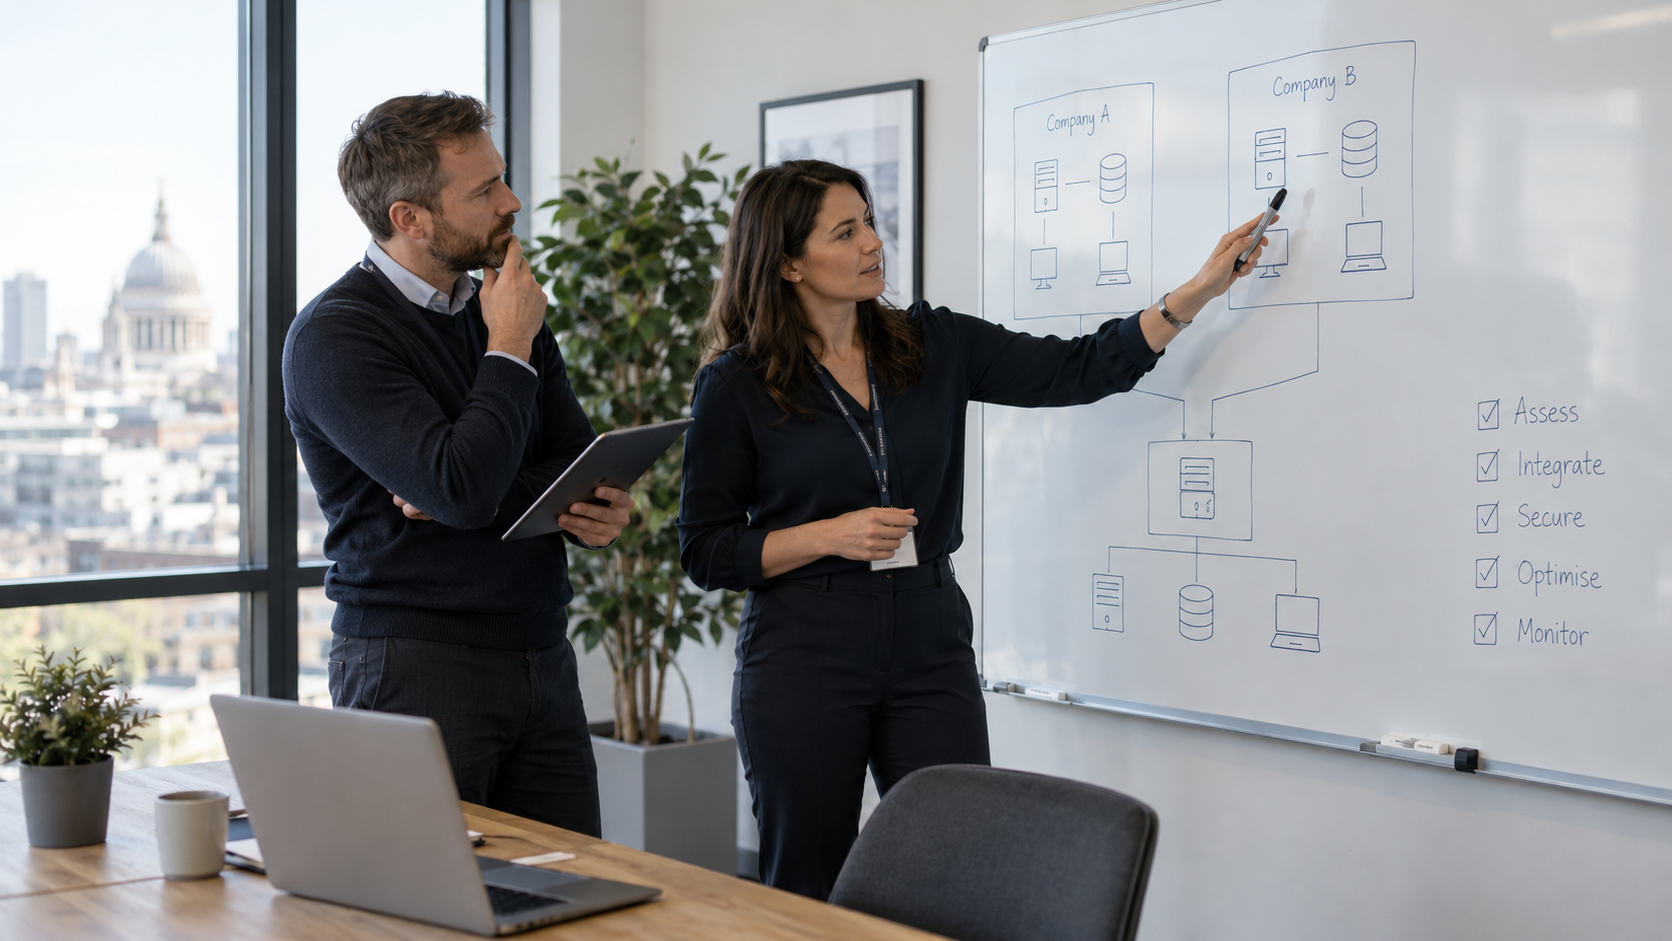
Specialist Focus: Dedicated exclusively to cybersecurity in M&A contexts, unlike generic due diligence providers
Financial Translation: Our methodology converts technical findings into tangible financial terms, supporting valuation
and negotiation
Regulatory Expertise: Deep knowledge of GDPR, NIS2, DORA, and UK–EU M&A frameworks ensure compliance and
governance integrity
Comprehensive Lifecycle Coverage: Supporting both pre-deal risk discovery and post-deal integration, we provide
continuity and resilience beyond the transaction
Download Our M&A Cyber Security Audit Leaflet
Download