The Pillars of Cyber Security
Book a free no obligation informal chat
Information supports customer service, business decisions and day-to-day operations. Protecting it requires attention to who can access it, whether it can be trusted and whether essential services remain usable when they are needed.
These five concepts offer a practical way to discuss information security: confidentiality, integrity, availability, authenticity and non-repudiation. They work together and should inform decisions about people, processes, technology and suppliers.
Confidentiality
Confidentiality protects information from being accessed or disclosed to people who are not authorised to receive it. For a business, this includes customer records, employee information, commercial plans and intellectual property. The aim is to make information available to the people who need it while protecting it from inappropriate exposure, whether it is stored, shared or processed.
Managers should identify sensitive information, assign an owner and define who needs access for their role. Review permissions when people join, move or leave, and give staff clear guidance on sharing information safely. Appropriate access controls, encryption and approved collaboration tools can support these decisions. Cloud services also need clear responsibilities and settings that match the sensitivity of the information being held.
Integrity
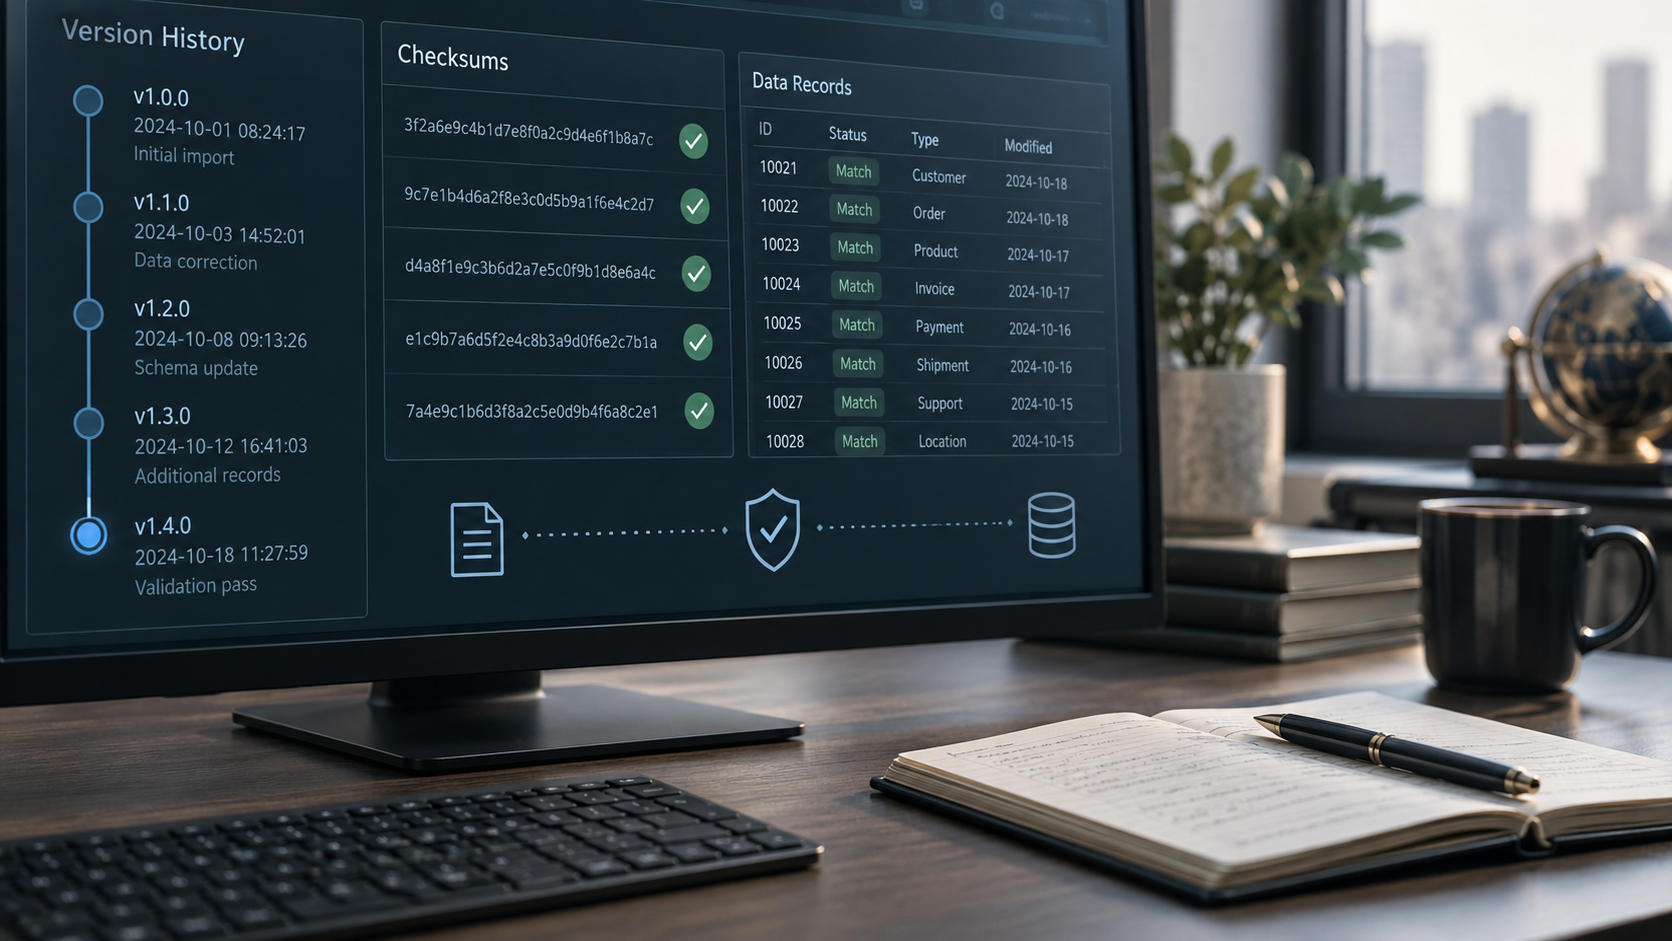
Integrity concerns the accuracy and consistency of information and protection against improper alteration or destruction. Business decisions depend on reliable records: an unauthorised change to a payment instruction, operational setting or customer record can cause harm even when the information remains confidential. Errors, equipment failures and deliberate interference can all undermine confidence in the data you use.
Define who may change important records and how those changes are approved and checked. Validation, version control and audit records can help identify mistakes and support investigation. Managers should know which data sources are authoritative and how discrepancies will be resolved. For critical processes, consider a second-person review so that a single error does not pass unnoticed into a business decision.
Availability
Availability means authorised users can access information and services reliably when they are needed. An organisation may protect its data well but still suffer serious disruption if staff cannot use the systems required to serve customers or run operations. Availability therefore needs attention to technology, suppliers and the people and processes on which essential services depend.
Identify the services whose interruption would have the greatest business impact and agree realistic recovery priorities. Maintain suitable backups and practise restoring them, alongside continuity arrangements for key systems and suppliers. Managers should understand acceptable downtime and who makes decisions during disruption. Exercises help establish whether recovery plans are workable and where investment or clearer responsibilities are needed.
Authenticity
Authenticity concerns confidence that a person, message or source is genuine. Authentication helps establish a claimed identity before access is granted; authorisation then determines what that identity may do. These are related but separate decisions. A message that appears to come from a trusted colleague or supplier still needs appropriate verification, particularly when it requests sensitive information or a financial change.
Use identity checks that reflect the risk of the activity and review account access throughout its lifecycle. For important requests, staff should know how to verify the sender through an established independent channel. Managers can reinforce this by making verification an accepted part of the workflow and ensuring employees can question unusual instructions without pressure to bypass agreed checks.
Non-repudiation
Non-repudiation concerns evidence that an action or communication took place and can be attributed to its originator. In digital transactions, this can help establish who sent or approved information and support later review of a disputed action. Digital signatures can contribute to this evidence; encryption alone does not establish who performed an action.
Identify the approvals and transactions for which your organisation needs dependable evidence. Consider how identities, timestamps and records are protected, who can access them and how long they are retained. Managers should define responsibilities for reviewing disputed activity and preserving relevant evidence. The value of those records depends on the reliability of the supporting processes and systems; a technical control does not by itself guarantee a legal outcome.
Definitions: NIST confidentiality, NIST integrity, NIST availability, NIST authenticity, NIST non-repudiation.