5 Challenges for Cyber Security
Book a free no obligation informal chat
Ensure That Contemporary Privacy Laws are Followed
Protecting personal information requires an understanding of what your organisation collects, why it uses it, where it is held and who can access it. UK data protection guidance calls for technical and organisational security measures appropriate to the risk. A cloud service can support those measures, but using it does not automatically establish compliance or remove the organisation’s responsibilities.
Managers should work with the privacy lead and IT team to map important data flows, review access and agree suitable retention arrangements. Consider the responsibilities of external providers and any international activities before sharing information. Record the decisions, give staff practical guidance and review controls when systems or working practices change. Where legal requirements are uncertain, obtain appropriate advice rather than assuming that a technology choice resolves them.
Defend Against Phishing Attacks
Phishing attempts to persuade someone to reveal information, open a harmful link or attachment, or authorise a payment. It can arrive through email or other messages and may impersonate a colleague, supplier or familiar organisation. Effective protection combines technical safeguards, secure account access and business processes that allow suspicious requests to be challenged.
Email authentication using SPF, DKIM and an appropriate DMARC policy can help reduce spoofing of your organisation’s domain. It does not make every message safe or prevent every form of impersonation. Give staff a simple reporting route, use multifactor authentication where appropriate and verify sensitive requests through an established independent channel. Managers should make it clear that unusual payment instructions can be paused for checking without pressure to bypass agreed procedures.
Bring-Your-Own-Device (BYOD) Policy
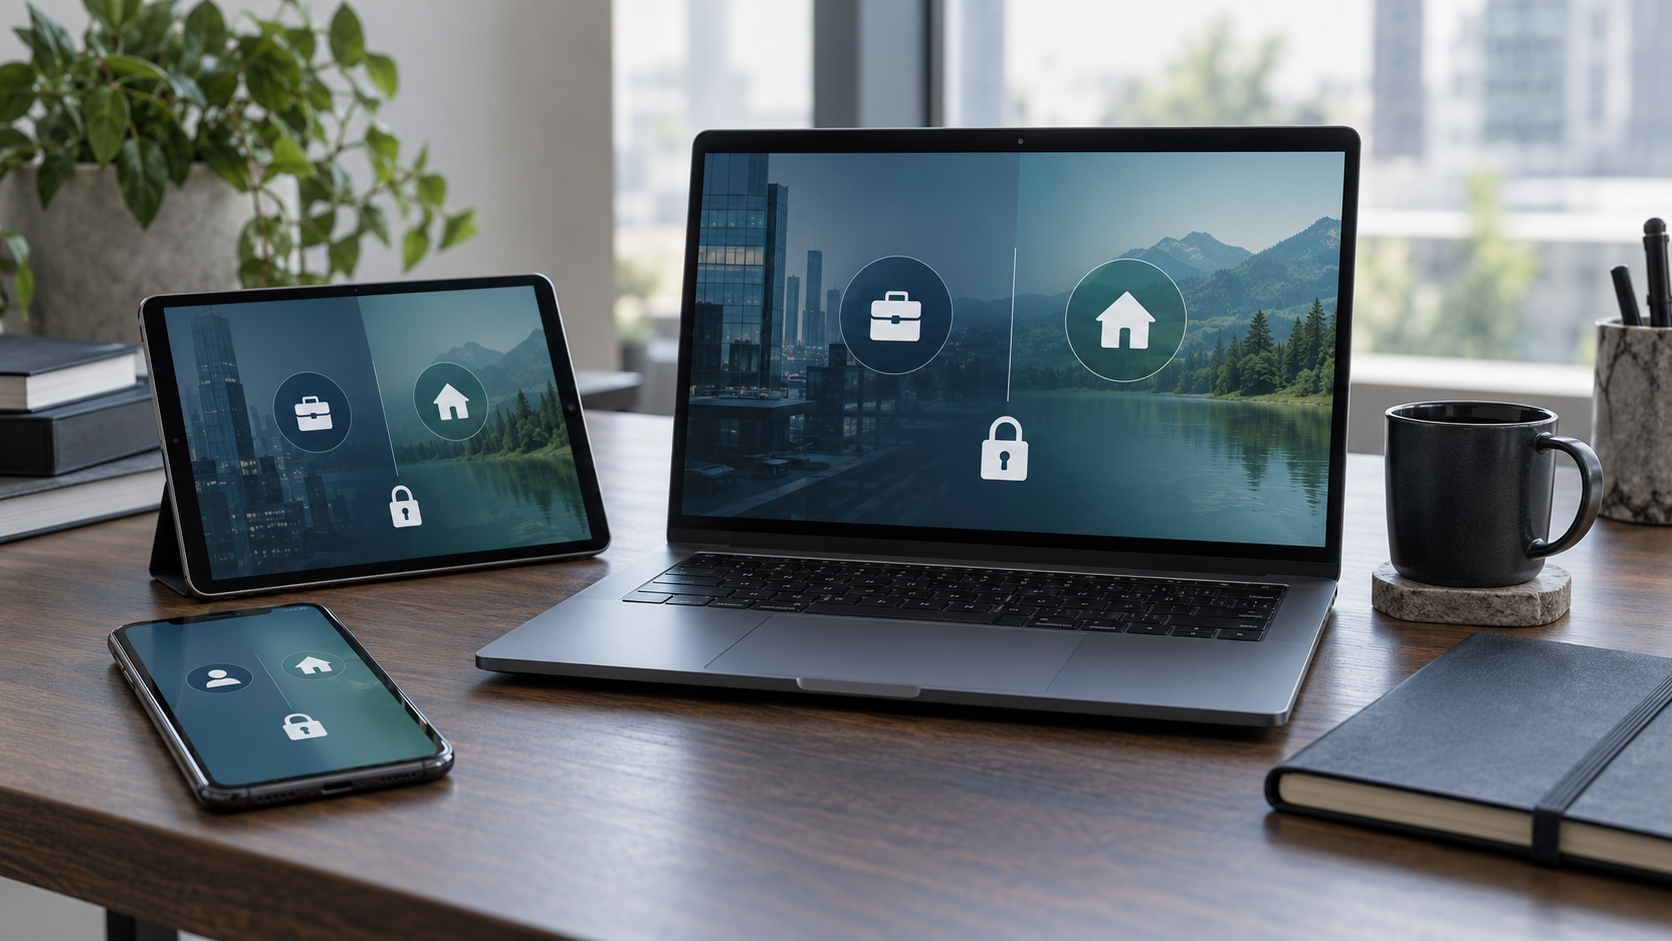
Bring-your-own-device arrangements allow employees to use personally owned phones, tablets or computers for work. The challenge is to protect business information while respecting the owner’s privacy and keeping the working arrangement usable. Different devices, software versions and support responsibilities need to be considered before access is granted.
Define which devices and services are permitted, the minimum security requirements and who provides support. Consider supported software, updates, strong authentication and suitable separation of work information from personal use. Explain what the organisation can manage or remove, particularly if a device is lost or a person leaves. Review the approach with IT and staff so that expectations are clear and controls match the sensitivity of the information being accessed.
Defending Against Ransomware Attack
Ransomware can prevent access to systems and information, while an associated attack may also involve data theft. The business impact can extend beyond IT to customer service, suppliers and essential operations. Preparation therefore needs both preventive controls and a workable plan for responding to disruption and recovering priority services.
Keep systems updated, restrict unnecessary access and maintain backups protected against alteration or deletion by an attacker. Regularly test restoration, including the dependencies needed to bring a service back into use. Managers should agree recovery priorities, incident responsibilities and communication arrangements before an event occurs. Exercising the plan helps identify gaps in supplier support, access to recovery information and the time needed to restore a usable service.
Blockchain and Cryptocurrency Attacks
Blockchain systems use distributed ledgers to record transactions, but the security of a ledger does not automatically protect every application or account connected to it. Organisations using cryptocurrency or other blockchain services need to consider private-key handling, the software they rely on and how transactions are authorised. These risks should be assessed in relation to an actual business use, rather than treating the technology as a universal requirement.
Before adopting a service, define who can approve transactions, how keys will be protected and what happens if access is lost or compromised. Review the provider, connected applications and any smart-contract functionality with suitable technical expertise. Consider monitoring and incident arrangements as part of the design. A clear operating model helps management understand where control rests and which risks need attention throughout the service’s lifecycle.
Conclusion
These challenges are best addressed through continuing management attention and practical controls. Start with the information and services that matter most to the business, then identify the weaknesses that could cause the greatest harm. Improvements should have clear owners, evidence of completion and a review date so that they remain effective as the organisation changes.
Bring business, IT and supplier representatives together to agree a manageable action plan. Use staff feedback, incidents and recovery exercises to check whether the arrangements work in practice. Oxford Systems can help you discuss your priorities and choose sensible next steps, from reviewing everyday security controls to planning a wider programme of improvement.